
Phishing Club


Phishing Club is a phishing simulation, training and red team phishing framework.
Quick start (production)
⚡ For systemd-enabled distributions, installation is quick and easy
Run the following on the server
curl -fsSL https://raw.githubusercontent.com/phishingclub/phishingclub/main/install.sh | bash
Remember to copy the admin URL and password
Production Docker Compose example
Features
Phishing Club provides a lot of features for simulation and red teaming, such as:
- Multi-stage phishing flows - Put together multiple phishing pages
- Domain proxying - Configure domains to proxy and mirror content from target sites
- Flexible scheduling - Time windows, business hours, or manual delivery
- Multiple domains - Auto TLS, custom sites and asset management
- Advanced delivery - SMTP configs or custom API Sender with OAuth support
- Recipient tracking - Groups, CSV import, SCIM provisioning, repeat offender metrics
- Awareness training - Run training campaigns that record started and completed, kept separate from phishing risk
- Campaign reports - PDF export with customizable HTML templates for phishing and training, automatically emailed on completion
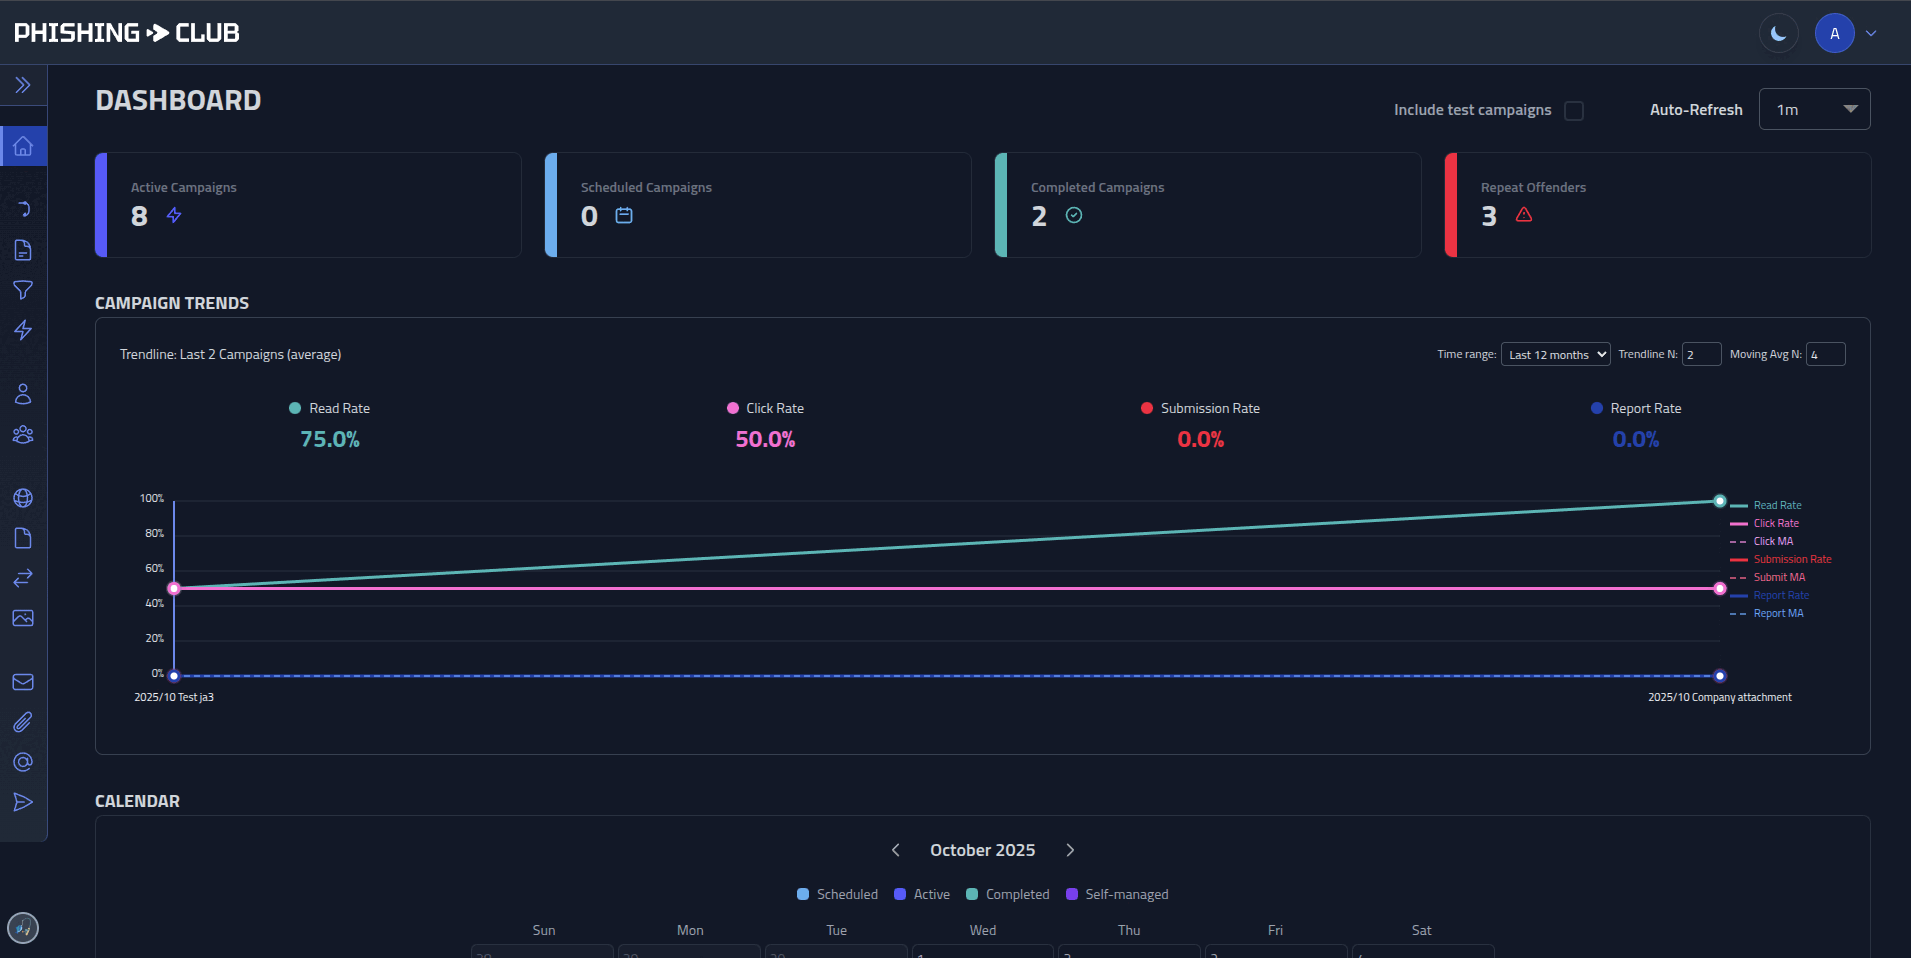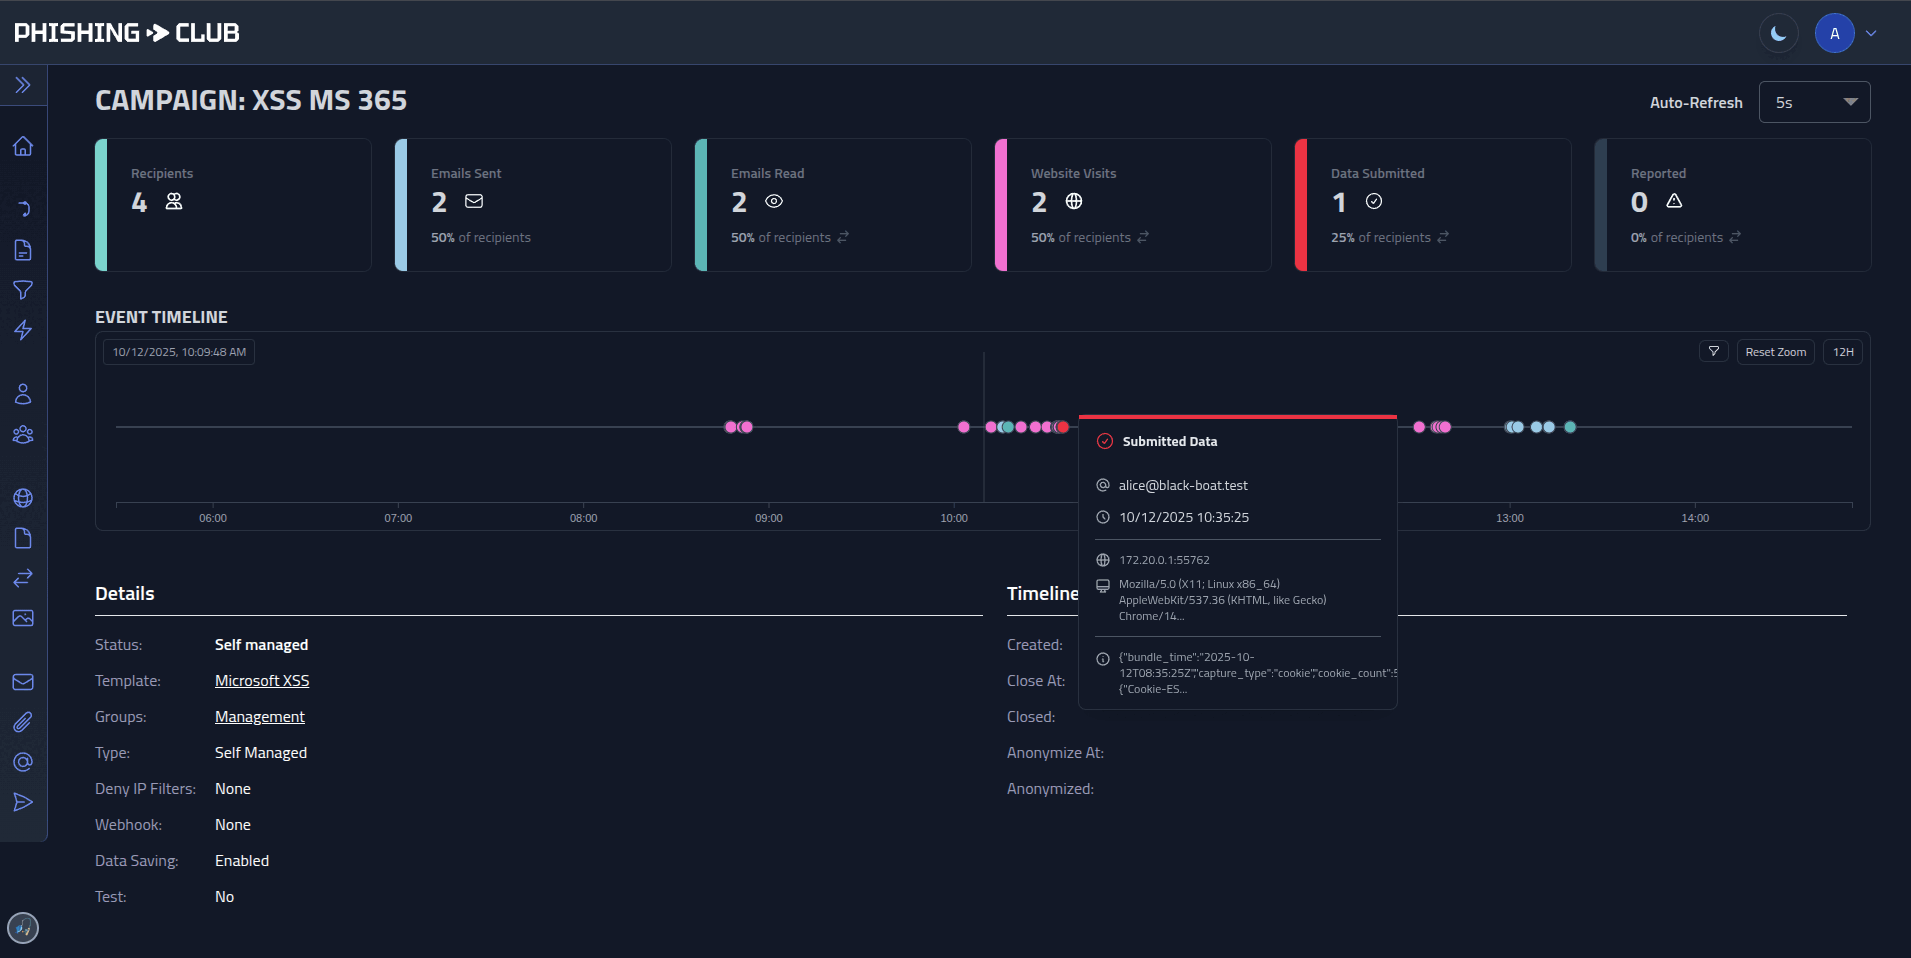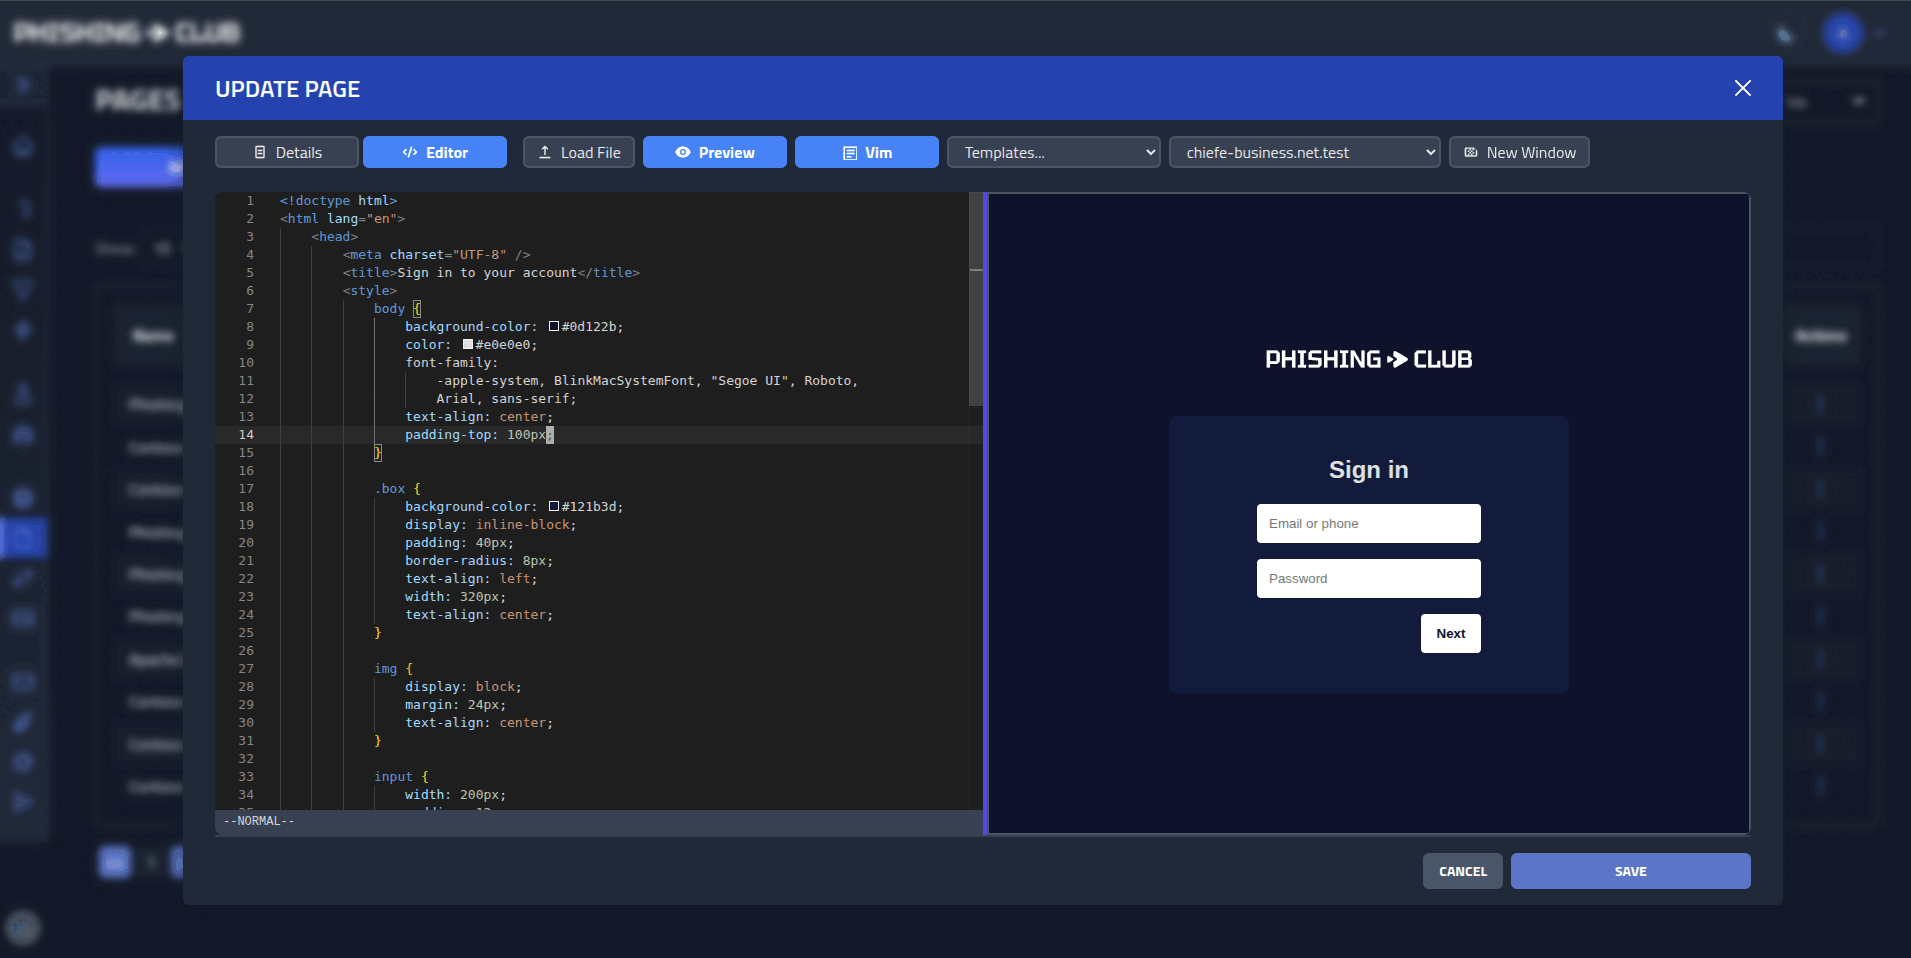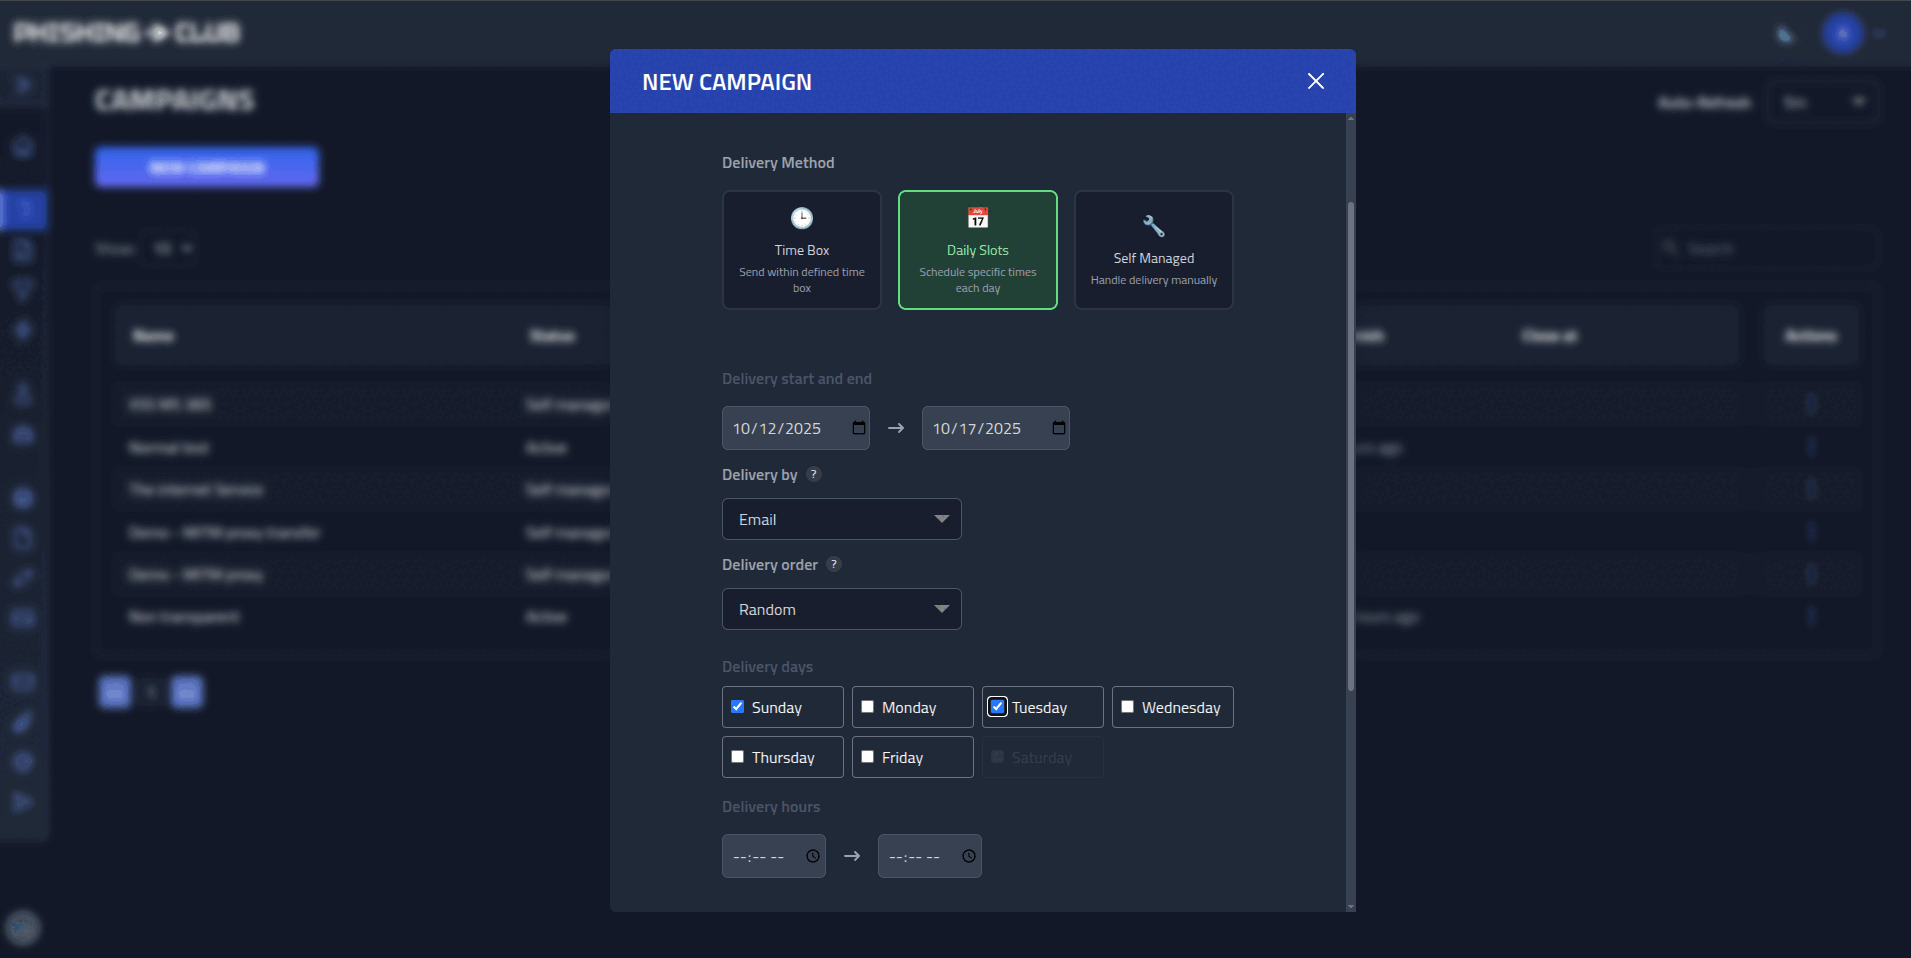
- Analytics - Timelines, dashboards, per-user event history
- Automation - HMAC-signed webhooks, REST API and embedded JavaScript scripting engine
- Multi-tenancy - Segregated client handling and statistics for service providers
- Anonymization - Pseudonymized campaigns, automatic anonymization on close and retention windows for compliance
- Branding - Replace logos and login image with your own
- Security features - MFA, SSO (Entra ID and OIDC), session management, IP filtering
- Operational tools - In-app updates, CLI installer, config management
AiTM and Red Team Features
- Reverse proxy phishing - Capture sessions to bypass weak MFA, import captured cookies with the Session Sushi extension
- Remote browser phishing - Stream and interact with a victim's live browser session
- Full control - Modify and capture requests and responses independently
- DOM rewriting - Modify content using CSS/jQuery-like selectors or regex
- Path and param rewriting - Rewrite URL paths and query parameters on the fly
- Dynamic obfuscation - Avoid static detection with dynamically obfuscated landing pages
- Evasion page - Customize the pre-lure evasion page
- Custom deny page - Decide what bots or evaded visitors see
- Access control - Default deny-list until visiting phishing lure URL
- Advanced filtering - Use JA4, CIDR and geo-IP to control lure URL access
- Browser impersonation - Impersonate JA4 fingerprints in proxied requests
- Response overwriting - Shortcut proxying with custom responses
- Forward proxying - Use HTTP and SOCKS5 proxies to ensure requests originate from the right location
- Visual Editor - Use the visual editor to easily setup a proxy
- Import compromised OAuth token - Use compromised tokens to send more phishing via OAuth enabled endpoints
- Device Code phishing - Device code phishing is as simple as adding a single line to a email or landing page
Blogs & Resources
- Phishing Club User Guide
- Covert red team phishing with Phishing Club
- Phishing Simulation vs Red Team Phishing: Understanding Different Approaches
- Remote Browser Phishing with Phishing Club
Wrote a blog post or write up about Phishing Club? Tell us about it and we might add it here. Reach out via a GitHub issue, discord or find our email :)
More from Phishing Club
Open source projects and learning resources built for students and red teamers.
Training Labs
Phishing Club Training Labs - Free hands on labs for adversary in the middle and remote browser phishing. Steal the session, not just the password. Capture credentials, hijack live sessions, and defeat real defenses like CSP pinning, beacon detection and passkey prompts.
Session Sushi
Session Sushi - A zero dependency browser extension for handling cookies, Microsoft 365 OAuth tokens, and Graph API interactions. Built for security professionals.
- Cookie Management - View, import/export as JSON, search, filter, and clear cookies, with incognito session support
- Microsoft 365 Sessions - Acquire OAuth tokens, store multiple M365 refresh tokens as sessions, refresh manually or automatically, and import/export sessions
- M365 Data Browsers - Graph, User, Directory, Mailbox, Calendar, OneDrive, SharePoint and Teams
Template Workbench
Phishing Template Workbench - A developer focused environment for creating and testing phishing simulation templates.
- Preview - See how templates render with test data
- Variable support -
{{.BaseURL}},{{.Email}},{{.FirstName}}substitution with realistic sample data - Naive Responsive Testing - Preview templates across mobile, tablet, and desktop
- Naive Email Testing - Check email templates in Mailpit and score HTML/CSS and SpamAssassin across clients
- Asset Management - Resolve template assets with fallback to global asset directories
- Export Ready - Copy processed HTML, download template folders, and export collections compatible with Phishing Club
Development
Run the whole stack locally with Docker and make:
git clone https://github.com/phishingclub/phishingclub.git
cd phishingclub
make up
make backend-password
Then open https://localhost:8003 and setup the admin account.
For prerequisites, service ports, make commands, local DNS and SSL setup, see DEVELOPMENT.md. For the contribution process, see CONTRIBUTING.md.
License
This project is licensed under the GNU Affero General Public License v3.0 (AGPL-3.0). This means:
- ✅ You can use, modify, and distribute the software freely
- ✅ Perfect for educational, research, and commercial use
- ✅ You can run your own instance for security testing or professional services
- ⚠️ Important: If you provide the software modified as a network service, you must make your source code available under AGPL-3.0
Contact reqarding license: license@phishing.club
Roadmap
There is no official roadmap.
But you can vote with emojis on the [feature] requests on Github or add your own feature request.
Feature request with a high number of votes will be prioritized, however it is no guaranteed they will be implemented. Ultimately what gets implemented, how and when highly depends on me and what I think is right for the project.
Contributing
We welcome contributions from the community! Please read our Contributing Guidelines
Quick Start for Contributors:
- Check existing issues and create a feature request if needed
- Wait for approval before starting work
- Fork the repository and create a feature branch
- Follow our development workflow and coding standards
- Submit a pull request with signed commits
For complete details, see CONTRIBUTING.md.
Suggestions for Contributors
- Improve or add templates to the template project
- Check existing feature requests - Want to work on something, make a comment.
Support
Need help? Join the Phishing Club Discord
Community support is provided on a best-effort, volunteer basis. For dedicated assistance, paid support is available.
- General Support: Join our Discord community or open a GitHub issue
- Security Issues: See our Security Policy
Security and Ethical Use
This platform is designed for authorized security testing only.
For important information about:
- Reporting security vulnerabilities
- Ethical use requirements
- Legal responsibilities
- Security best practices
Please read our Security Policy.
Important: Users are solely responsible for ensuring their use complies with all applicable laws and regulations.